Installation AD CS connection
To connect Appterix to the Microsoft PKI, it is sufficient if the domain controller has been assigned the AD CS role.
When installing the EgoMind AD Sync Service, a certificate template for Windows SmartCard authentication (Appterix SmartCard Logon) is automatically created in AD CS.
When using AD CS in the enrollment of Appterix YubiKey Management, the Appterix Agent (client component) sends the certificate request to AD CS via the Appterix server components so that the certificate is created and provided. The certificate is then written to the selected YubiKey.
Download AD Sync Service
You can download the current AD Sync Service in the Appterix Management UI under Downloads > Additional component.

During the installation, Installation credentials for of of the respective AD connector from the EgoMind Platform
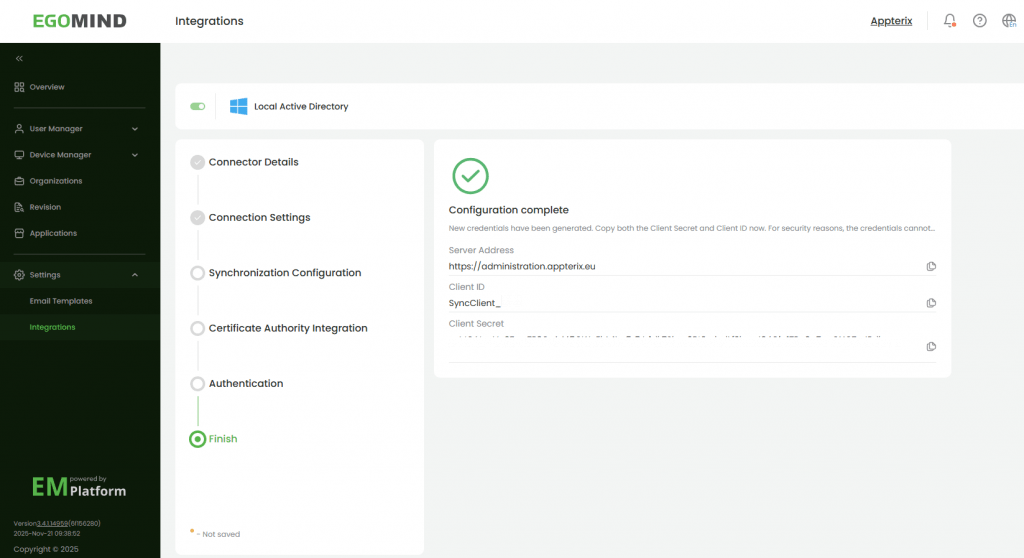
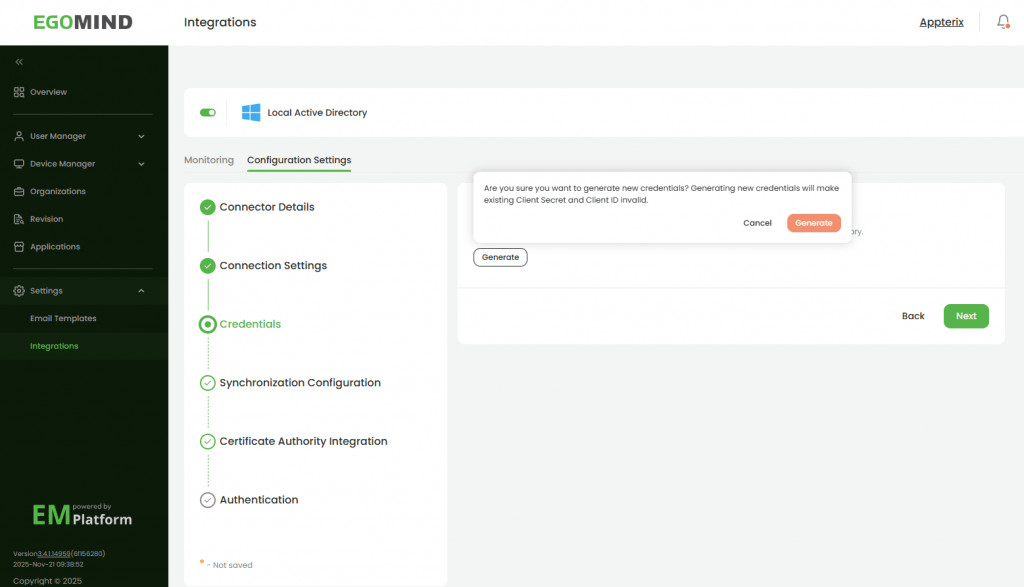
Connection to AD certificate authority
After you have installed the AD Sync Service and logged in with the login data of the respective AD connector , please check whether the synchronization is working correctly.
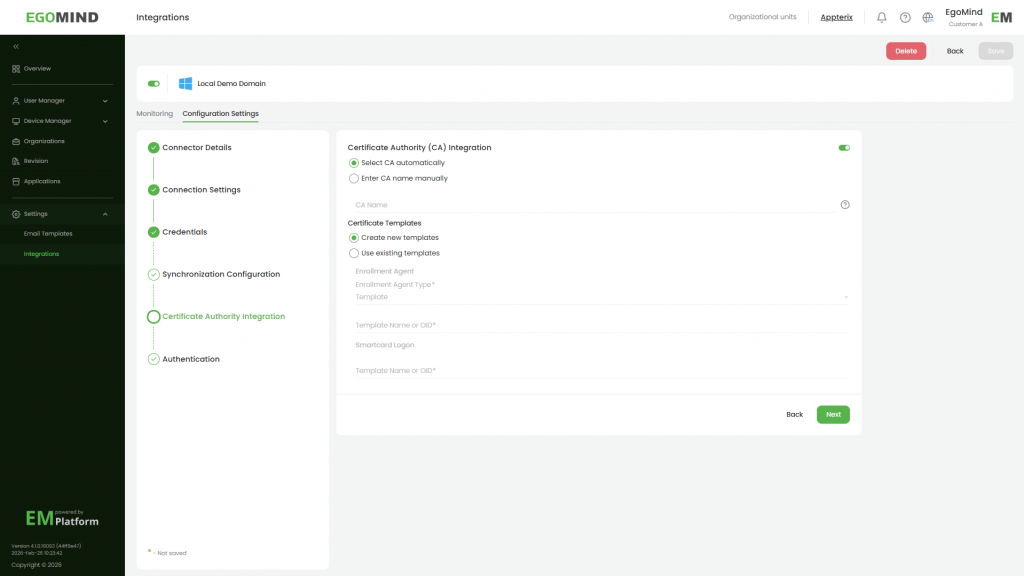
You can then check whether there are in your AD Certificate templates the templates Appterix Smartcard Logon and Enrollment Agent. If this is not the case, please check whether in the User import member of the AD group Certificate Issuer. is specified. If not, we recommend that you go to the Appterix installation directory and navigate to the ADSyncService/Utils (in the standard C:\Program Files\EgoMind\EMADSyncService\Utils ) and there open the EMADSyncService.ControlPanel as logged into Windows Enterprise Administrator .
There you will find the AD CS Connector Area where you enter the name of the AD user specified in the EMPlatform for synchronization, who had previously logged into the system, as well as the domain and CA name.
The certificate template will then be found.
If the certificate template is available but the Enrollment of AD CS Certificates is not be possible, it may be because the in the EgoMind platform under Settings / User Import stored user information did not allow authentication to the domain or the user did not have group membership as Certificate Issuer. Please use the format domain\user
If you have multiple AD certificate authorities you can use in the User import or in AD Sync Control Panel the CA Name of the certification authority to be used. If you leave the field CA Name blank , the domain controller will use the first listed AD certificate authority .

Further information
- Set up AD CS connection:
https://appterix.eu/help/zertifikatbasierte-authentifizierung/